Cybersecurity
Avatec approaches cybersecurity as part of the operational technology lifecycle—from product selection and architecture to commissioning, maintenance and recovery.
Singapore OT approach
Secure by deployment, not only by product
Singapore’s OT cybersecurity direction recognises that resilient operations depend on people, process and technology working together throughout design, deployment and maintenance. For Avatec systems, this means defining the real operational need for every connection, controlling how equipment joins the customer’s network and maintaining a clear support route after handover.
Architecture and access
Keep critical power visible without making it unnecessarily exposed
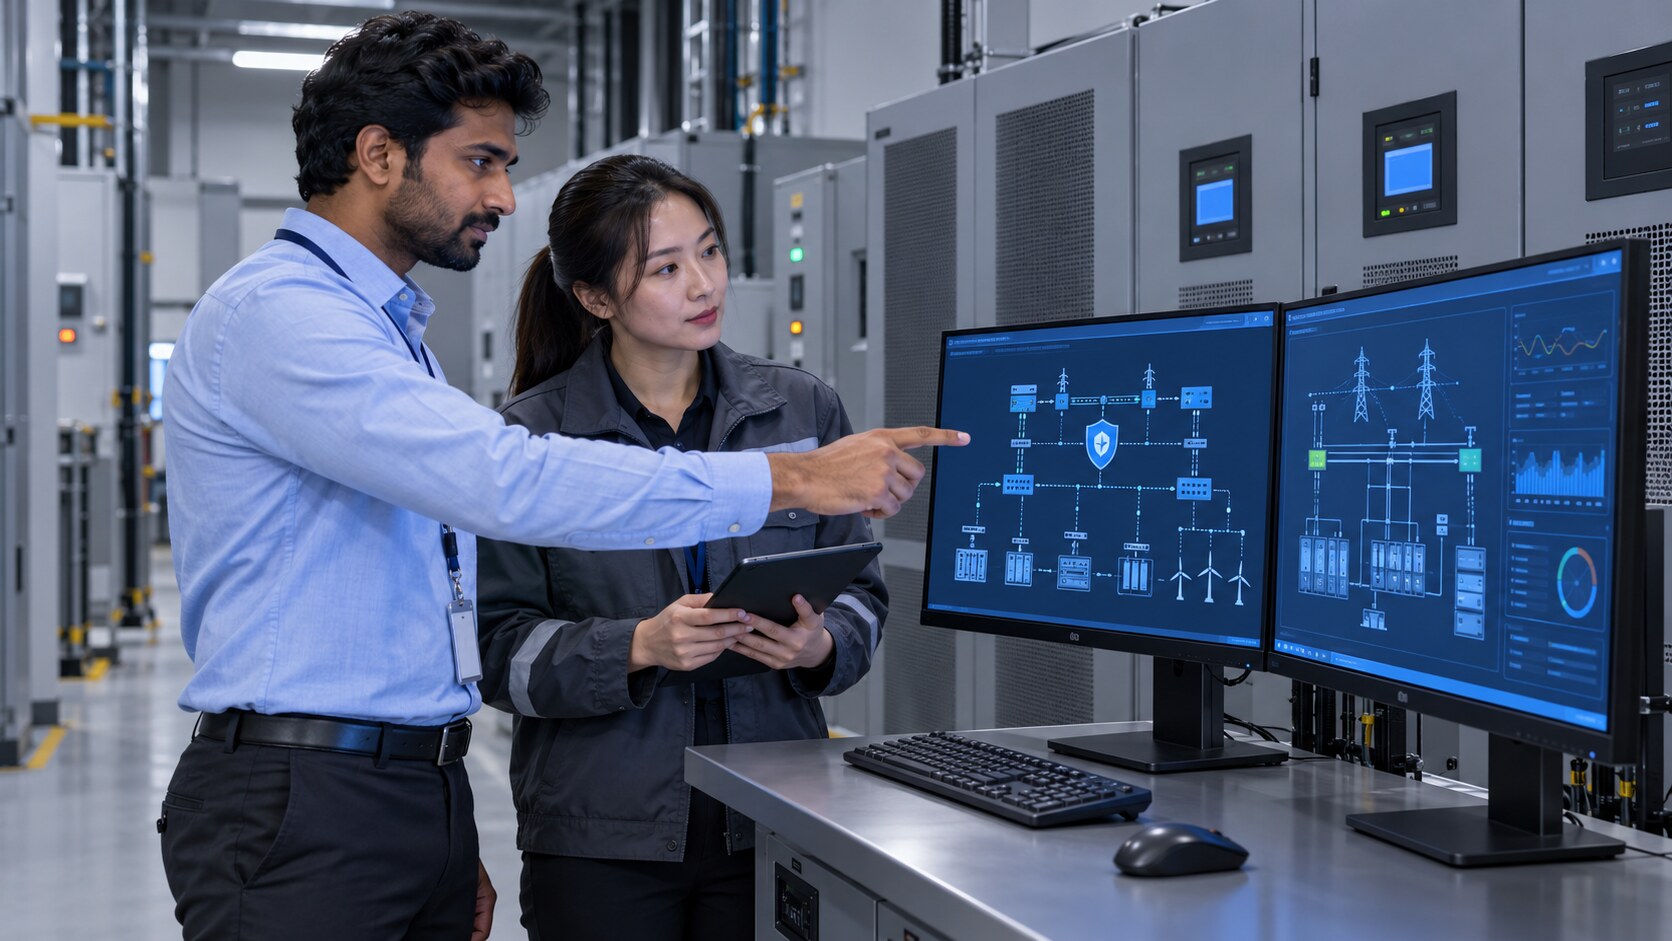
UPS, charger, inverter and battery monitoring data may be required by a local HMI, building-management system, distributed control system or secured remote operations platform. Avatec defines the required data path and avoids enabling interfaces that are not needed.
Connected equipment should sit within the owner’s OT zones and conduits, separated from business and public networks by approved security controls. Administrative access is limited to authorised roles; default credentials are changed; remote access follows the owner’s controlled method; and network ports, protocols and accounts are recorded at handover.
Secure commissioning
Establish a known and recoverable baseline
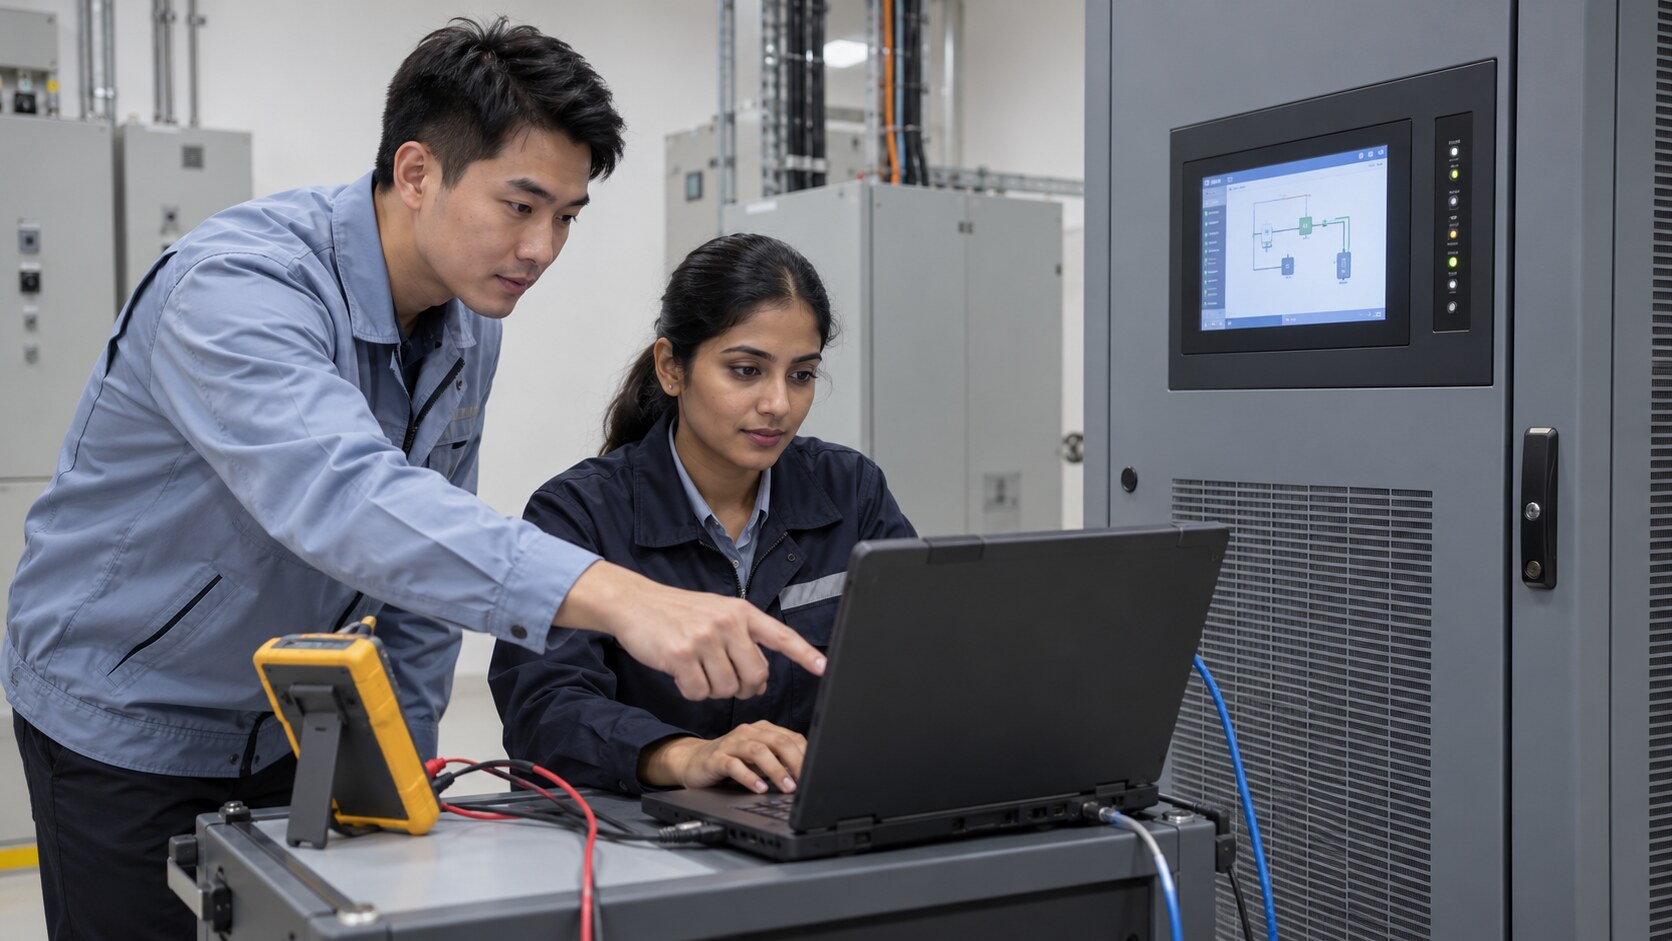
Cybersecurity checks are included with functional commissioning when networked features are in scope. The team confirms addressing, enabled services, account ownership, time settings, event records, communications to approved systems and the ability to restore the agreed configuration.
- Asset, firmware and communication-interface inventory.
- Approved configuration and parameter backup.
- Role and account register with ownership defined.
- Controlled laptop, removable-media and service-access practices.
- Documented connection to customer monitoring and alarm systems.
Operation, updates and response
Maintain security without compromising availability
Changes, firmware updates and vulnerability actions are assessed against operational risk, redundancy, service windows and recovery arrangements. Known-good configurations are backed up, the authorised change is recorded, functional checks are defined in advance and a rollback method is prepared before work begins.